Networking
20 Fortinet Firewall Interview Questions: Policies, Routing and Troubleshooting
Prepare for FortiGate interviews with 20 practical answers covering policies, NAT, VPN, HA and traffic diagnosis, plus a scenario and preparation checklist.
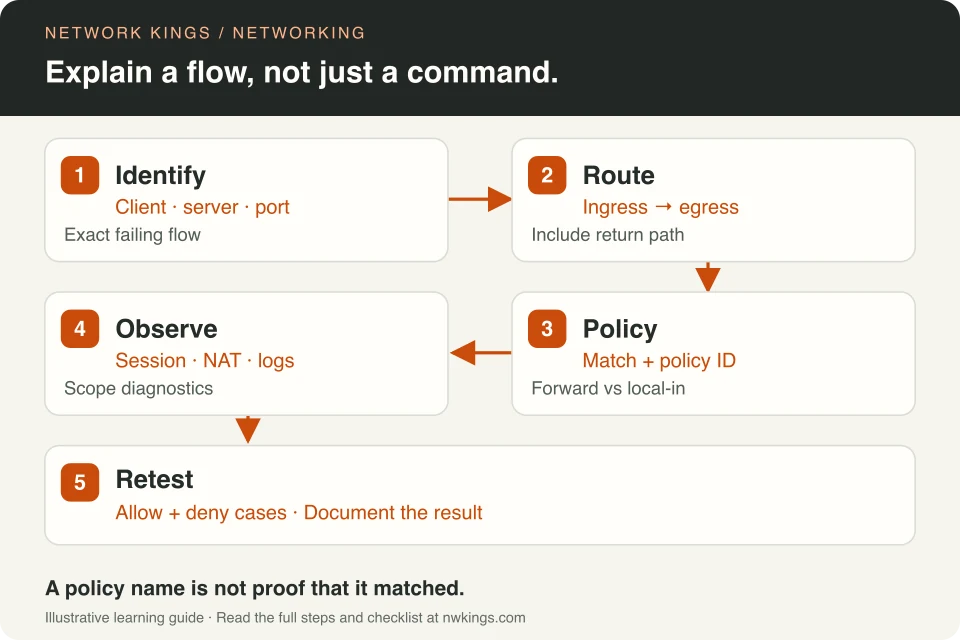
Strong Fortinet firewall interview answers connect a feature to a traffic path, observable evidence and a verification step. Explain how you would identify the affected flow, inspect routing and policy, check sessions or logs, make a justified change and retest. These 20 original practice questions cover FortiGate operations; they are not exam dumps or a claim about an employer's interview questions.

Examples refer to FortiOS 7.6 documentation unless a source explicitly identifies another release. Menu labels, defaults and diagnostic behavior can vary by build, hardware, VDOM and inspection mode. State your assumptions in an interview instead of treating one lab's settings as universal.
Foundational FortiGate questions
1. What is FortiGate, and what is FortiOS?
FortiGate is Fortinet's firewall platform; FortiOS is its operating system. Explain the security functions relevant to the deployment—traffic control, VPN and configured inspection—without assuming every licensed service is enabled. A useful follow-up is to ask about hardware, virtual deployment, firmware and operational scope.
2. What does a stateful firewall remember?
It tracks permitted sessions and uses that state when handling related traffic. A session entry can help explain how a connection is being processed. However, state does not eliminate the need for correct routing, valid policy or a functioning destination. Distinguish an existing connection from a newly created one when testing a change.
3. How does a firewall policy match traffic?
For the relevant policy type and mode, inspect interfaces, addresses, service, schedule and any identity conditions. Policies are ordered; a broader rule can match before a more specific one. Identify the actual policy ID from evidence rather than assuming that the rule's name proves it handled the packet. Refer to Fortinet's policy guide for the release's behavior.
4. What does implicit deny mean?
For forwarded traffic, a flow without an applicable permitting firewall policy is denied. Do not generalize this to every traffic category: management traffic destined to the FortiGate itself involves interface administrative access and local-in controls. “I added a forward policy” does not establish that management access is restricted correctly.
5. What is a VDOM?
A virtual domain separates logical firewall operation within a FortiGate deployment. When investigating a flow, confirm that you are viewing the intended VDOM and its interfaces, routes and policies. Checking a healthy route in another VDOM is not evidence for the failing flow.
Routing, NAT and traffic questions
6. What would you check when a permitted policy still has no traffic?
Confirm the source is generating the intended request, then observe whether it reaches the expected ingress interface. Check the active route and egress decision, earlier policies, addressing and service. A zero hit count may mean the flow takes another path, never arrives, or does not match; it does not by itself identify the cause.
7. How are source NAT and destination NAT different?
Source NAT changes the source addressing seen farther along a flow, often for outbound access. Destination NAT changes the destination mapping, commonly through a configured virtual IP. In either case, describe original and translated tuples, the relevant policy, and the return path. Translation alone is not permission to pass traffic.
8. What changes when central SNAT is enabled?
Source translation is controlled through the central SNAT table rather than the ordinary per-policy NAT option. Fortinet documents top-down matching in that table and mode-specific behavior. In an interview, say you would verify central-NAT status before interpreting the policy's NAT fields. See the central SNAT guide.
9. Why does asymmetric routing complicate troubleshooting?
The request and reply can traverse different devices or interfaces, so the stateful firewall observing one side may not see the expected session progression. Draw both directions and inspect the actual paths before recommending a workaround. A route change that restores symmetry can be more appropriate than relaxing a protection without understanding its purpose.
10. How do you separate DNS failure from application failure?
Record the resolver's answer, the destination address actually used and the requested port. Then correlate an approved service test with firewall and application evidence. A DNS answer only proves a name resolved. A successful TCP connection only proves a transport connection; neither proves authorization or the application's response is correct.
Diagnostic and security questions
11. Which tools would you use to inspect a flow?
Start with logs and session information. A packet sniffer shows observed packets on selected interfaces; debug flow helps explain processing decisions. Fortinet's CLI reference lists relevant commands. Choose a narrow filter and bounded capture rather than collecting unrelated traffic.
12. What would a scoped debug-flow example look like?
On an isolated, authorized training firewall, the following illustrates an IPv4 filter for a fictional client. Verify syntax on your release and coordinate with other operators before resetting diagnostics. The trace count bounds the diagnostic; always stop it afterward.
diagnose debug reset
diagnose debug flow filter clear
diagnose debug flow filter addr 192.0.2.10
diagnose debug flow show function-name enable
diagnose debug flow trace start 10
diagnose debug enable
# Generate the single authorized test request, then stop:
diagnose debug disable
diagnose debug flow trace stop
diagnose debug flow filter clear
13. Why might debug flow show less than expected?
A filter, existing session, wrong VDOM or hardware offload can affect visibility. Fortinet's 7.4.3 debug-flow guide explicitly discusses processor offload limitations. Treat that as a release-qualified caveat; use the appropriate platform documentation before changing offload behavior. Do not disable acceleration globally merely to make a trace look busy.
14. What is the difference between flow and proxy inspection?
They represent different inspection approaches, with feature support and behavior depending on the profile and release. Describe what the selected mode does for the actual traffic and which security profiles are applied. Avoid declaring one universally faster or more secure without a workload, hardware and feature context.
15. Does attaching an IPS profile guarantee protection?
No. Verify that the flow matches the intended policy, the profile is active, relevant signatures and actions are configured, and logs show the expected test result. Encrypted traffic and inspection choices affect what can be observed. A profile name in a configuration is evidence of configuration, not proof of effective detection.
VPN, high availability and change questions
16. What if an IPsec tunnel is up but traffic fails?
Separate tunnel establishment from data delivery. Check the intended local and remote networks, route selection, applicable firewall policies, NAT requirements, traffic counters and the far-side return path. Record which side sees the test flow. An established tunnel does not prove every destination subnet is reachable.
17. What does HA session pickup do?
It synchronizes supported session information to help preserve connections during failover. It does not promise zero interruption for every protocol or session type. Fortinet's session-pickup documentation distinguishes supported behavior and configuration. Validate a representative application during an approved failover test.
18. How would you prepare a firmware upgrade?
Identify the exact model and firmware, read release notes and the supported upgrade path, back up the configuration securely, define rollback criteria and schedule a maintenance window. Record pre-change interface, routing, VPN, HA and application health. Repeat those checks after each required upgrade stage rather than treating a successful reboot as completion.
19. How would you explain SD-WAN troubleshooting?
Identify the application's requirements, candidate links, health-check results and the rule selecting the path. Compare expected and observed path selection with latency, loss or availability evidence relevant to that rule. “Both links are up” does not establish that the desired service is healthy or that the traffic is using the intended member.
20. What belongs in a change and handoff note?
Record the affected flow, timestamp and timezone, original evidence, justified change, rollback plan, test result and remaining uncertainty. Remove credentials and unnecessary packet payloads from shared records. Give the next engineer enough context to repeat the test without recreating your investigation from scratch.
Work through one interview scenario
A fictional branch client can reach its gateway but cannot reach an approved web service. Describe your investigation aloud: confirm the URL, DNS answer and port; observe ingress; inspect the selected route and policy ID; examine translation and replies; then check server behavior. If the log identifies a deny caused by the wrong source object, propose the narrow correction and retest an allowed and an intentionally denied case.
A good answer explains what each observation rules out and what remains unknown. A weak answer lists commands, adds an any-to-any rule and stops when one ping succeeds. Practise describing a failed hypothesis as clearly as a successful repair.
Your practical checklist
Use these checks here or download the matching checklist.
- Identify the model, FortiOS build, VDOM and inspection assumptions.
- Explain policy matching and distinguish forward traffic from local-in access.
- Draw original and translated tuples and both routing directions.
- Use logs and narrowly scoped diagnostics for one authorized test.
- Explain why offload or session state may change diagnostic visibility.
- Separate VPN establishment and HA configuration from application success.
- Define rollback and pre/post-change checks.
- Prepare one evidence-based scenario answer without exposing credentials.
Choose your next learning step
Review network fundamentals, explore FortiGate firewall training, and use networking practice labs to build a scenario you can explain.
Book a career guidance callback to discuss your starting skills, or compare current learning plans and fees. Confirm the syllabus, lab access and enrolment details on the chosen program page.
Sources and editorial note
- Fortinet: policies, FortiOS 7.6.6
- Fortinet: central SNAT, FortiOS 7.6.6
- Fortinet: CLI troubleshooting, FortiOS 7.6.0
- Fortinet: debug-flow visibility, FortiOS 7.4.3
- Fortinet: local-in controls, FortiOS 7.6.1
- Fortinet: session pickup
Technical references checked on 18 October 2026. By Network Kings. Prepared with AI assistance; no independent technical review recorded. Worked scenarios are illustrative learning exercises, not a claim of completed target-platform testing or learner outcomes.